
Introducing AI Governance in Lema
Lema gives you visibility and control over AI sprawl across your third-party ecosystem. It discovers all AI providers and native-AI tools in use, whether approved or not, assesses the exposure, monitors how it changes, and helps you take action.


Watch now


Most of Your AI Arrived Without a Review

Vendors add AI after you assesed them, and employees adopt AI tools without going through approval at all.
Learn how Lema's AI Governance discovers third-party AI, assesses the exposure it creates, and surfaces where real-world usage has drifted from what was approved.


What We'll Cover

See AI Governance in Lema: how we discover AI across the vendor ecosystem, assess it, map model and fourth-party dependencies, and monitor what changes
AI inventory
Shadow AI that was never approved and new AI capabilities added after a vendor was assessed

AI assessment
Capabilities, data use, model providers, fourth parties, and the controls that matter
Continous monitoring
New models, agents, subprocessors, data practices, and scope changes

Remediation
Product settings, access changes, vendor requests, contract terms
Introducing AI Governance in Lema

Tomer Roizman
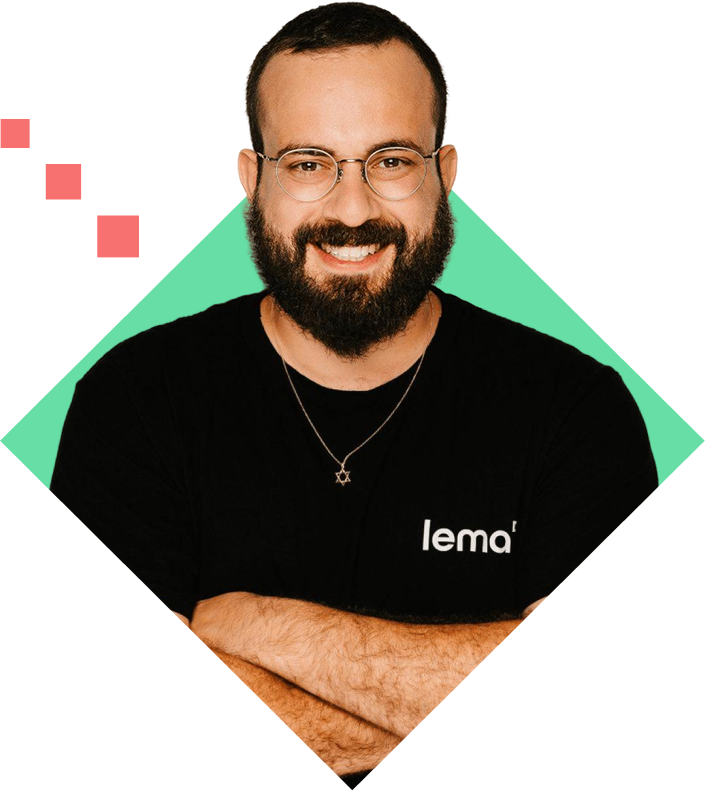
Tomer co-founded Lema to bring evidence-based, engineering-driven thinking to third-party risk. He works at the intersection of vendor intelligence and real-world usage data, focused on helping GRC and security teams move past checkbox reviews toward finding the risks that actually matter.

Craig Riddell
Craig leads security at Lema. He previously served as CISO at Netwrix and as Field CISO at Wallarm, and has spent his career helping enterprise security teams translate technical risk into business decisions.
AI Adoption Isn’t Waiting on Security
Register now to get visibility and control over the AI already spreading across your vendor ecosystem.