Third-Party AI Governance
Visibility and control over third-party AI sprawl
Discover all the AI across your vendor ecosystem, approved or not. Understand the exposure, monitor what changes, and take action.
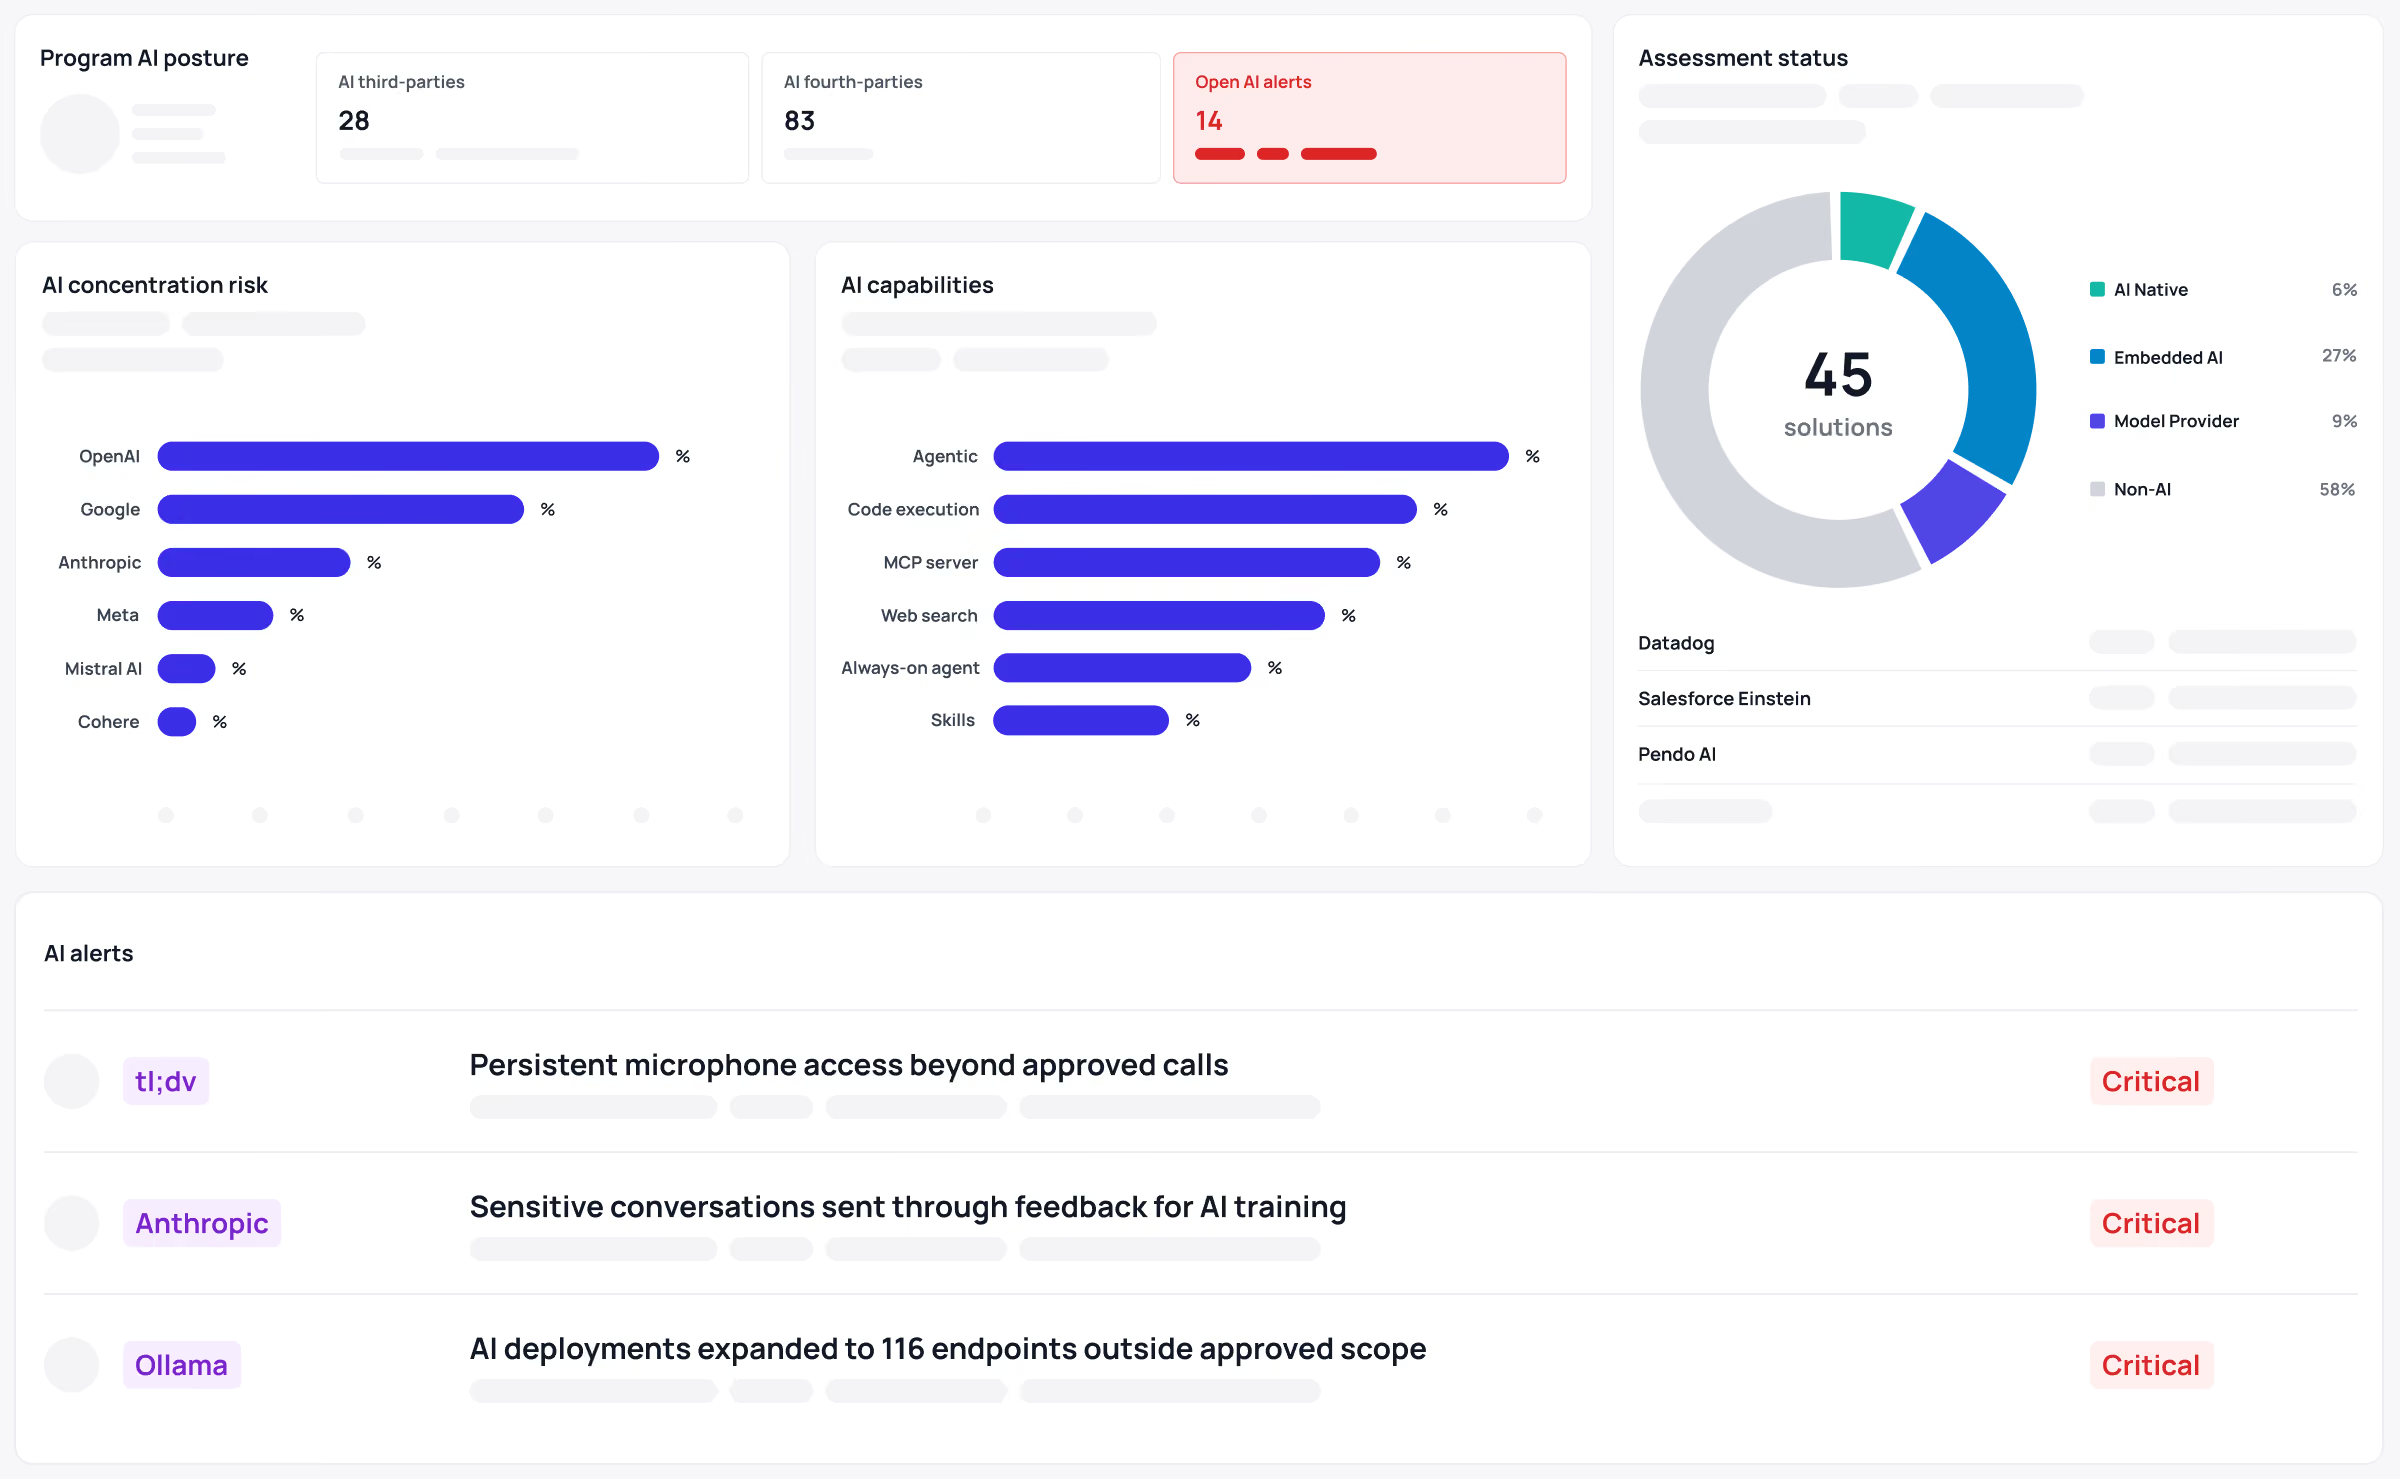
AI adoption isn't waiting on security
New AI tools are entering the organization. Existing vendors are adding AI capabilities. Products approved for one use are introducing new models, agents, subprocessors and data practices.

Approved vendors
add AI
You approved the vendor for one use. It has since added AI that was never assessed.

Vendors change
models
Vendors you approved for AI switch model providers, add capabilities, or change how they use your data.

Shadow
AI
AI tools arrive through SaaS, browser extensions and OAuth grants without any review.
CONTINUOUS MONITORING
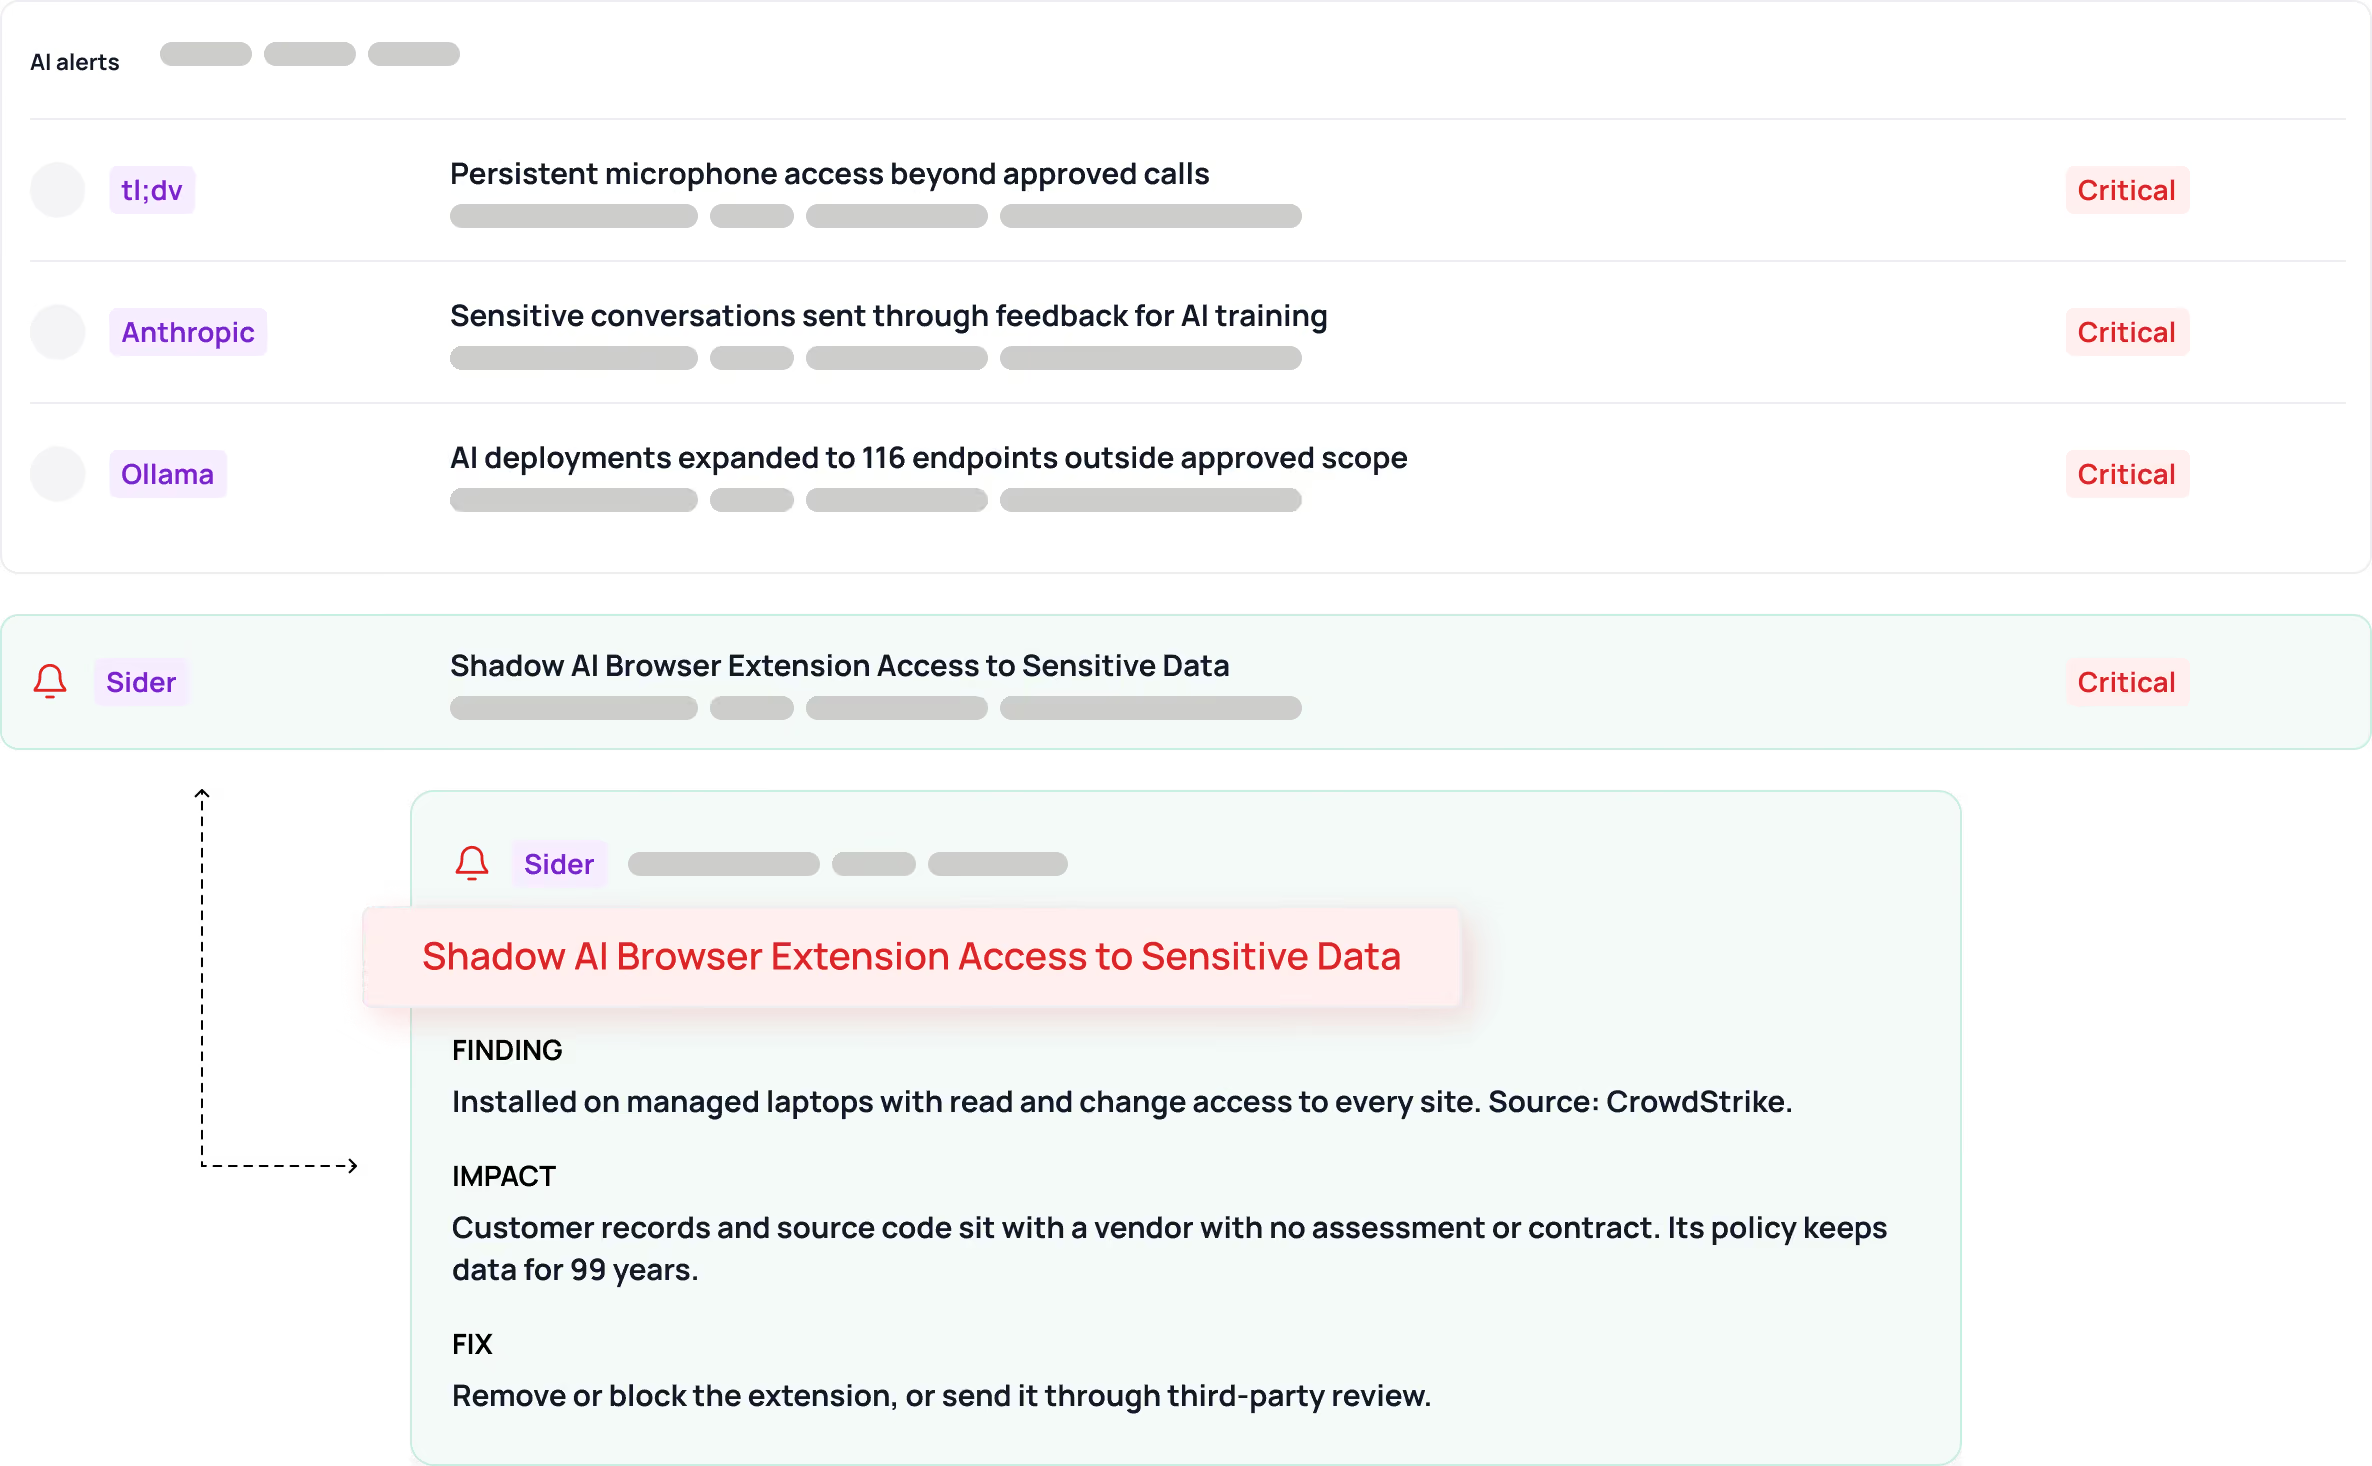
Know when your AI exposure changes
Know when new AI appears, vendors add AI capabilities, introduce new model providers, change how they use your data, enable autonomous capabilities, or expand beyond the approved scope.
COMPLETE VISIBILITY
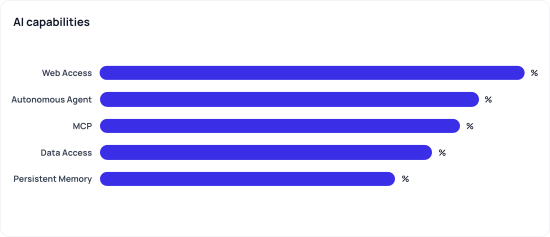
Understand AI type, capabilities, and access
Automatically detect AI capabilities, such as agentic behavior, code execution, MCP, and web access. Drill down into how the AI is being used, including its intended and approved use.
CONCENTRATION RISK
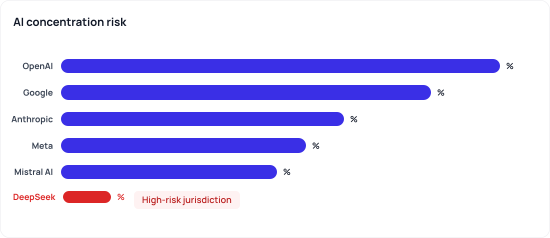
See the model providers behind your vendors
Map the providers behind your vendors and see where shared dependencies create portfolio-level exposure.
FORENSIC AI ASSESSMENTS
Validate what your vendors are telling you
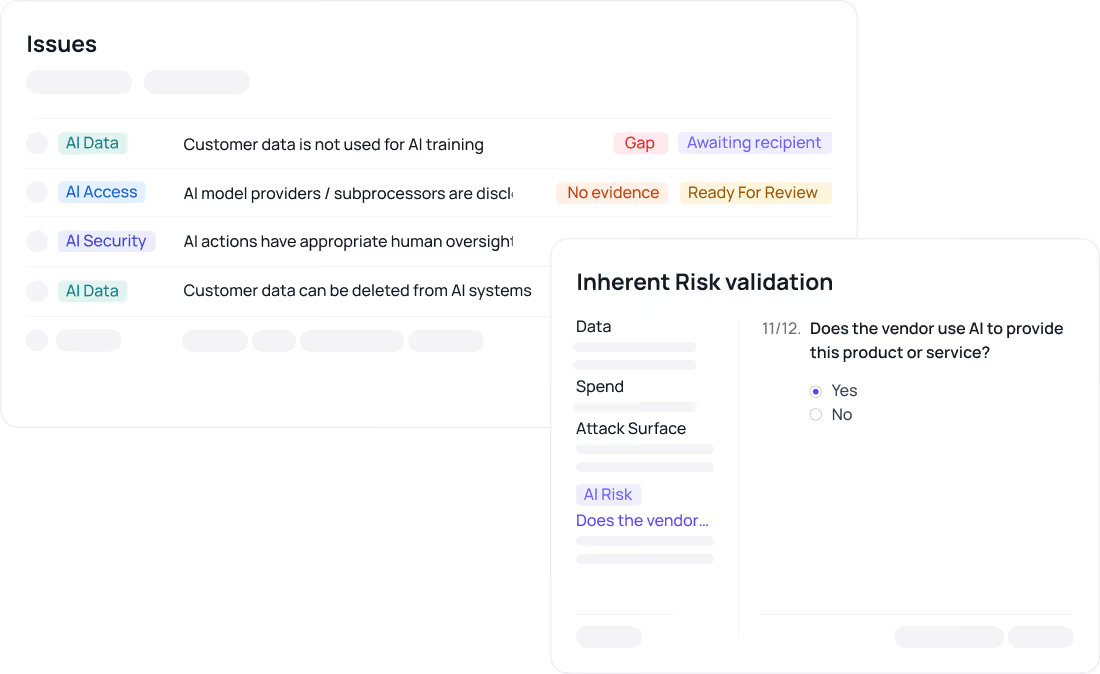
Validate vendor claims and collect evidence without relying on vendor assertions alone.
Assess AI vendors against AI-specific controls, with out-of-the-box frameworks like NIST AI RMF or a custom framework of your choice.